Mastering the CPTS Exam: A Complete Guide to opennms, Drupal, Rocket Chat, selfservicestg, hrportal, and gogs Machines
cpts opennms drupal rocket The CPTS exam is designed to evaluate a penetration tester’s ability to exploit real-world systems under pressure. Unlike theoretical certifications, CPTS focuses on hands-on hacking and practical troubleshooting. To succeed, candidates must be comfortable working across a variety of platforms — including opennms, Drupal, Rocket Chat, selfservicestg, hrportal, and gogs machines — each simulating realistic attack surfaces found in modern environments.
Understanding the CPTS Practical Approach cpts opennms drupal rocket chat selfservicestg hrportal gogs
The CPTS exam challenges you with a full attack chain: enumeration, exploitation, privilege escalation, and post-exploitation. Each machine in the lab represents a different technology stack, requiring exam-takers to think creatively and adapt quickly.
Below is how each required keyword system plays a role in exam-style scenarios.
1. opennms Machines: Monitoring Tools as Attack Vectors
opennms environments often expose sensitive network monitoring endpoints. In a CPTS-style challenge, misconfigurations or outdated plugins can reveal credentials, SNMP weaknesses, or escalation opportunities.
Mastery of common enumeration scripts and service-based privilege escalation techniques is essential.
2. Drupal Machines: CMS Attacks and Module Exploitation
Drupal systems in CPTS scenarios frequently require:
- Module enumeration
- SQL injection chains
- Remote code execution via vulnerable extensions
Drupal’s security history makes it a perfect target for demonstrating structured CMS exploitation.
3. Rocket Chat Machines: Messaging Platforms in Pentests
With Rocket Chat, exam candidates must understand:
- API enumeration
- WebSocket analysis
- Authentication bypass techniques
- Misconfigured admin interfaces
These machines highlight modern communication platforms and their typical weaknesses.
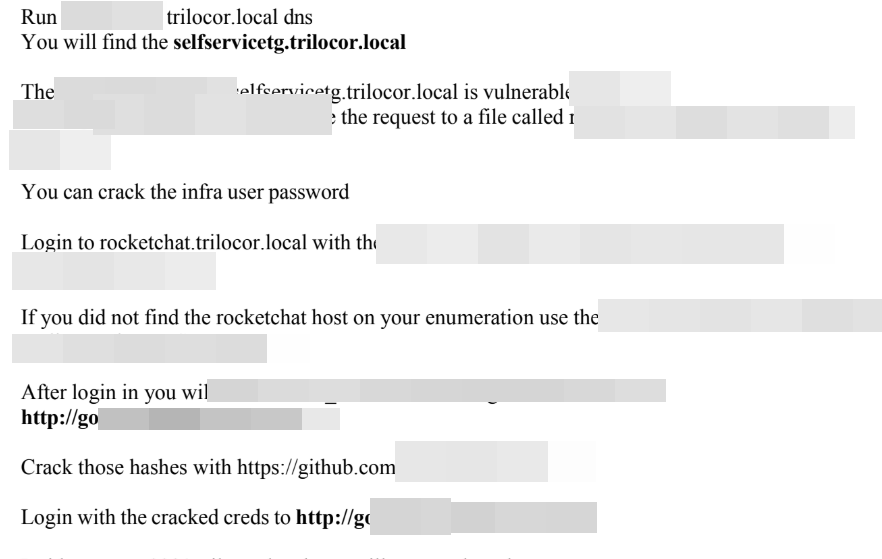
4. selfservicestg and hrportal Machines: Corporate Workflow Exploits cpts opennms drupal rocket
Applications like selfservicestg and hrportal simulate internal enterprise portals.
Typical CPTS exam vectors include:
- Weak session handling
- Insecure direct object references
- Poorly sanitized form inputs
- SSRF or command injection risks
These machines enhance your ability to assess business-critical systems.
5. gogs Machines: Source Code Repositories as Attack Surfaces cpts opennms drupal rocket
A gogs (self-hosted Git service) machine commonly involves:
- Default credentials
- Git repository leaks
- CI/CD misconfiguration flaws
- Arbitrary command execution
Understanding repository security is crucial as many real attacks originate from developer platforms cpts opennms drupal rocket chat selfservicestg hrportal gogs machines.
Conclusion: Building the Skillset for CPTS Success !
The CPTS exam rewards candidates who can adapt rapidly across multiple technologies. By practicing on opennms, Drupal, Rocket Chat, selfservicestg, hrportal, and gogs machines, you build a well-rounded exploitation mindset that mirrors professional penetration testing.
A structured study plan — including enumeration mastery, exploit development, and privilege escalation techniques — will position you strongly for CPTS success.
Get the material: CPTS exam material
Vendor : https://academy.hackthebox.com/