The best cybersecurity certifications for pentesting share one trait: they force you to break into real systems and document the whole engagement, not tick boxes on a multiple-choice sheet. That single filter cuts a crowded field down to a short list of lab-based exams that mirror a live client assessment — exploitation, Active Directory abuse, lateral movement, privilege escalation, and a professional report that gets graded. This list selects for that hands-on realism, transparent exam structure, and hiring recognition for penetration tester and red-team roles, then maps each credential to the experience level and time budget it actually suits.
We run Cyber Services for exactly the people this list is written for: practitioners who know where they want to land and want mentor-backed, exam-aligned preparation instead of months of unstructured trial and error. Below are three credentials that align tightly with pentesting work, each with its distinction, its ideal fit, and its honest limitations.
Table of contents
How we selected these pentesting certifications
A credential earns a place here only when it proves offensive skill under conditions that resemble a real engagement. We applied six criteria, and every certification below clears all of them.
- Fully practical exam format. The assessment is hands-on with no or minimal multiple choice, so a pass reflects demonstrated exploitation rather than recall.
- Realistic scope. Enterprise networks, Active Directory, web exploitation, and formal reporting are all in play, not isolated puzzle boxes.
- Published structure. The exam window, target set, and reporting requirements are clearly documented so candidates can plan an engagement timeline.
- Hiring recognition. The credential signals capability to hiring managers filling penetration tester and red-team positions.
- Level fit. The certification serves a defined experience band, from newer practitioners to seasoned operators.
- Efficient preparation paths. Focused, mentor-supported guidance exists so time-constrained candidates can compress study without wandering.
That last point is where we spend our energy. Our mentor-backed materials cover the OSCP, CPTS, and PNPT tracks with targeted writeups and instant delivery, so preparation stays aligned to what the exam actually tests. If you already know your target, you can jump straight to the matching resources in the Cyber Services store.
OSCP: the enterprise gold standard for hands-on pentesting
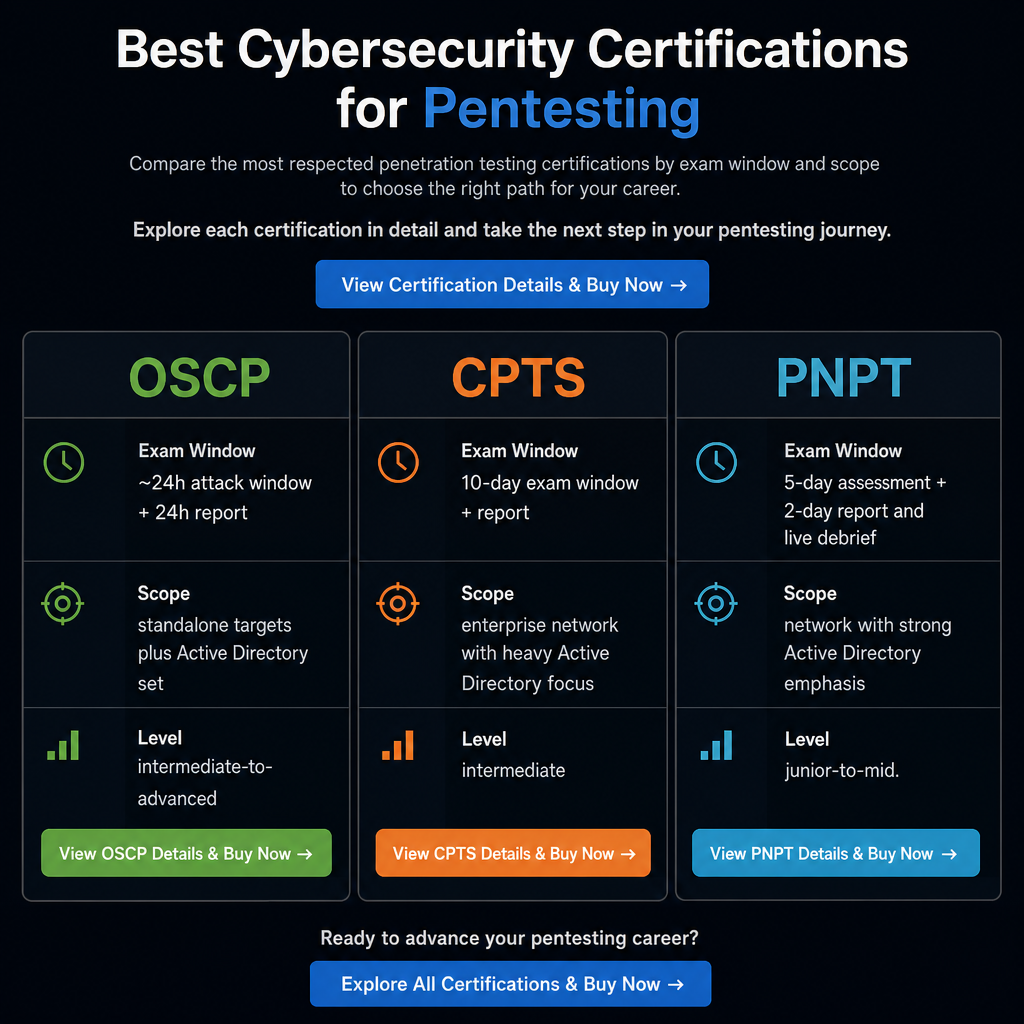
Wondering which certification opens the most doors in large consultancies? OSCP (OffSec Certified Professional) is attached to the PEN-200 course, Penetration Testing with Kali Linux, and it validates your ability to identify, exploit, and escalate vulnerabilities across a controlled lab with practical Kali-based methodology rather than theory. The exam is entirely practical: roughly 24 hours of attack time across multiple machines — including an Active Directory set and standalone targets — followed by an additional 24 hours to write and submit a detailed report.
Who it fits. OSCP is widely treated as a gold standard for penetration testing in larger enterprises and consulting firms because it proves you can run an engagement independently and document it end to end. It suits intermediate-to-advanced learners who already understand networking, Linux, and basic scripting, since those are explicitly recommended foundations. If your target is offensive-security consulting, internal red teaming, or high-stakes bug hunting, OSCP gives hiring managers a strong, immediately recognized signal.
Where it hurts. The format is demanding. A 24-hour exam plus the reporting period is mentally and physically draining, especially for people holding down a full-time job. There are no formal prerequisites, but weak Linux or scripting skills make the curve steep and stretch preparation time considerably. The core OSCP does not expire once earned, which is good for a long-term resume; the trade-off is that some holders drift out of practice if they stop testing regularly. The newer OSCP+ variant carries an expiration policy, so confirm which credential a given role expects.
For professionals targeting OSCP with limited spare hours, we provide mentor-supported OSCP exam support materials and a structured OSCP preparation checklist built to compress learning into focused, exam-aligned practice. If you want the credential without months of self-guided guesswork, that is where to start.
HTB CPTS: a long-window, AD-heavy enterprise engagement
Prefer several days to think over a single overnight sprint? The HTB Certified Penetration Testing Specialist (CPTS) from Hack The Box assesses intermediate penetration-testing skills across an enterprise-style network. Training and exam span the full lifecycle — reconnaissance, initial access, lateral movement, privilege escalation, and professional reporting — mapped to recognized methodologies such as PTES and OSSTMM. The exam gives you a 10-day window to compromise an enterprise network with significant Active Directory focus and produce a professional report that is graded as part of the assessment.
Who it fits. CPTS is built for learners who want realistic practice in an AD-heavy environment but prefer a multi-day window over OSCP’s 24-hour push. It expects at least a foundational grasp of networking and core offensive techniques, since Hack The Box positions it as validating intermediate rather than entry-level skill. It is regarded as high value for its price, with comparatively affordable vouchers and tight integration with HTB Academy modules — a strong practical option when you want depth without a four-figure training bill.
Where it hurts. Ten days plus report writing is still a serious commitment for anyone juggling family or on-call duties. The AD-heavy scope delivers excellent enterprise realism but can overwhelm candidates with limited Windows or domain-security background, converting into extra fundamentals prep. Recognition is climbing fast, yet CPTS is newer than legacy names, so some hiring managers may not yet recognize the acronym even when they value the skills behind it.
If you plan to sit CPTS but want to cut trial and error, our exam-aligned CPTS preparation resources and mentor-guided insight focus you on the attack paths, reporting style, and scope that actually appear in the assessment. You can also review the CPTS certification price breakdown before you commit a voucher.
PNPT: a realistic multi-day pentest with debrief and free retake
Want an exam that feels like a real consulting project rather than a puzzle hunt? The Practical Network Penetration Tester (PNPT) from TCM Security is fully practical and explicitly avoids multiple-choice and CTF-style challenges. It emulates a client engagement: a 5-day assessment window against a network with strong Active Directory emphasis, followed by 2 days to produce a professional report and deliver an executive-style debrief. Course materials are included in the base price, and PNPT offers one free retake — a philosophy of not profiting from failure.
Who it fits. PNPT matches junior and mid-level practitioners who want a narrative-style engagement over a puzzle grind. Its focus on Active Directory, lateral movement, and clear reporting makes it useful preparation for internal security teams and smaller consultancies where network pentesting is a core duty. The cost sits well below many legacy certifications, giving budget-conscious candidates a credible practical credential without a heavy training invoice.
Where it hurts. The friendlier price and free retake do not lower the skill floor. PNPT still expects a solid foundation in networking, Windows domains, and common offensive tooling; underestimating that leads to rushed or incomplete reporting. Recognition is growing rapidly, especially in small and mid-sized organizations, but may not yet match OSCP’s long-standing status inside some large enterprises. The multi-day format plus report and debrief demand disciplined time management — a weak timeline plan leaves you scrambling to finish documentation inside the reporting window.
For candidates who want to pass efficiently, our PNPT-focused writeups and mentor support show how successful candidates structure attack paths, reports, and debriefs, so you can replicate proven approaches instead of starting from a blank page.
How to choose the right pentesting certification for you
The right credential is the one that fits your goal, your calendar, and your stamina. Map yourself against the drivers below before you buy a voucher.
| Your situation | Strongest fit | Why it lands |
|---|---|---|
| Breaking in from a junior IT or security role | PNPT, then CPTS | Realistic scope with a friendlier ramp before OSCP’s intensity |
| Proving enterprise-ready skill for consulting or senior roles | OSCP | Immediate recognition in large enterprises and consultancies |
| You handle intense single bursts | OSCP | 24-hour attack window plus report suits a concentrated push |
| You prefer spreading effort across days | CPTS or PNPT | 10-day and 5-day windows leave room to reflect and recover |
| Budget-conscious with retake safety | PNPT | Lower price point and one free retake reduce financial risk |
A practical sequencing rule: if Active Directory and professional reporting still feel unfamiliar, build those muscles on PNPT or CPTS before OSCP, then use OSCP to signal enterprise readiness. Whichever target you set, pairing it with mentor-supported resources shrinks the hours lost to unrelated labs and keeps your effort on the exact attack chains, objectives, and reporting style the exam grades. When you are ready to commit, browse our pentesting certification support portfolio for OSCP, CPTS, and PNPT preparation with instant delivery.
Frequently Asked Questions
Which pentesting certification should I start with if I am new?
If you are comfortable with basic networking and operating systems but new to offensive security, an accessible practical certification focused on fundamentals, followed by PNPT or CPTS, is usually more manageable than jumping straight into OSCP’s intensive format.
Do employers really care about hands-on exams?
Yes. OSCP, CPTS, and PNPT stand out because they require you to compromise real systems and write a professional report, which signals real-world capability far more strongly than a purely multiple-choice exam.
How long should I plan to study?
Most candidates budget several months of focused study for OSCP and at least a few intensive weeks for CPTS and PNPT, depending on starting skill and familiarity with Active Directory, exploitation, and reporting.
Can mentor-supported resources reduce my study time?
Structured, mentor-guided materials aligned to exam objectives remove much of the guesswork, especially for time-constrained professionals, by pointing you to the techniques, attack chains, and reporting habits that matter most. Our resources combine instant delivery with targeted writeups and a success-oriented support model for exactly that purpose.
Once you have chosen your target, the next step is securing exam-aligned, mentor-backed preparation. Explore our store for OSCP, CPTS, PNPT, and other offensive-security resources to move from aspiring to certified with less wasted time.