OSWP Exam Review 2026: Difficulty, Format and Preparation
OSWP Exam Review 2026 examines the OffSec Wireless Professional certification, including its practical exam format, difficulty, wireless security topics, reporting requirements, and preparation strategy. Based on OffSec’s published PEN-210 exam rules, candidates face three wireless network scenarios, receive 3 hours and 45 minutes for the practical assessment, and have an additional 24 hours to submit their report.
OSWP is a specialized certification for penetration testers and network security professionals who want to demonstrate hands-on wireless security skills. Unlike broader certifications such as OSCP, it concentrates on IEEE 802.11 networks, wireless authentication, encryption weaknesses, traffic analysis, and professional documentation.
OSWP Exam Review: Quick Overview
The OffSec Wireless Professional (OSWP) certification is associated with PEN-210: Wireless Network Attacks.
| Exam detail | Current requirement |
|---|---|
| Certification | OffSec Wireless Professional (OSWP) |
| Training course | PEN-210: Wireless Network Attacks |
| Practical exam | 3 hours and 45 minutes |
| Reporting window | Additional 24 hours |
| Available scenarios | 3 wireless networks |
| Passing requirement | Complete 2 scenarios, including the mandatory one |
| Exam environment | Remote, proctored laboratory |
| Reporting format | Professional PDF report |
| Main focus | Wireless network assessment and security |
The official exam guide is the authoritative source for requirements and restrictions. Always review it before scheduling an attempt.
What Is the OSWP Certification?
OSWP validates practical skills in identifying and assessing wireless network security weaknesses.
The certification focuses on technologies and concepts used in Wi-Fi environments, including wireless standards, network discovery, authentication, encryption, packet analysis, and access point security.
OffSec’s PEN-210 course also introduces wireless assessment tools and the security implications of rogue access points and wireless configuration weaknesses.
This OSWP Exam Review focuses on what those skills mean for exam readiness rather than presenting confidential exam solutions.
For the current syllabus, visit the official OffSec PEN-210 course page.
OSWP Exam Format and Passing Requirements
One of the most important parts of any OSWP Exam Review is understanding the assessment structure.
According to OffSec, the exam provides three wireless network scenarios. Candidates can work on only one scenario at a time through the examination control panel.
Each scenario requires candidates to assess the target wireless environment and meet the objectives described in the official exam instructions.
Passing requires successfully completing two scenarios, including the one identified as mandatory.
The examination is practical, meaning candidates must demonstrate technical skills rather than answer a traditional multiple-choice questionnaire.
How Long Is the OSWP Exam?
The practical assessment lasts 3 hours and 45 minutes.
After the practical window closes, candidates have a separate 24-hour period to upload their professional report.
These deadlines make time management, organized note-taking, and accurate evidence collection essential.
Is the OSWP Exam Proctored?
Yes. OffSec provides a proctored examination environment with a designated remote laboratory.
Candidates should verify their examination setup, connectivity requirements, and permitted tools using the latest official documentation.
How Difficult Is the OSWP Exam?
OSWP Exam Review discussions frequently focus on difficulty, but the answer depends heavily on the candidate’s familiarity with Linux and wireless networking.
OSWP has a narrower technical scope than a general penetration testing certification. However, that does not make it automatically easy.
Candidates must understand wireless protocols, interpret captured traffic, distinguish network configurations, and work efficiently under a short time limit.
What Makes OSWP Challenging?
Wireless fundamentals. Candidates need to understand how access points, clients, channels, authentication, and encryption interact.
Technical accuracy. Misinterpreting a wireless configuration or captured data can lead to incorrect conclusions.
Time management. The practical examination window is relatively short, leaving limited room for disorganized troubleshooting.
Documentation. Completing technical objectives is not enough if the required report lacks evidence.
Tool familiarity. Candidates should understand the tools permitted by OffSec and avoid depending on prohibited automation.
The most reliable preparation is repeated, independent practice in authorized wireless laboratories.
Technical Topics Covered in PEN-210
The OSWP Exam Review should be understood in the context of the PEN-210 training syllabus.
Wireless Networking and IEEE 802.11
Candidates should understand wireless network terminology, access point behavior, client associations, radio channels, and the purpose of different 802.11 frame types.
These fundamentals are essential for interpreting wireless traffic accurately.
WEP, WPA and WPA2 Security
PEN-210 covers wireless encryption technologies and security weaknesses associated with different configurations.
Candidates should understand the differences between legacy encryption, pre-shared-key authentication, and stronger enterprise security designs.
Learning why particular configurations are weak is more valuable than memorizing the behavior of one laboratory environment.
Wireless Traffic Analysis
Traffic analysis helps security professionals understand wireless communications and recognize relevant authentication and management activity.
Tools such as Wireshark, Kismet, and the Aircrack-ng suite appear in the broader PEN-210 curriculum.
Candidates should become comfortable interpreting results and distinguishing valid evidence from incomplete observations.
Rogue Access Points and Wireless Misconfigurations
Rogue access points and incorrectly configured wireless networks can create risks involving unauthorized connectivity, user trust, and network segmentation.
PEN-210 introduces these topics through controlled exercises.
For real-world assessments, testing must be explicitly authorized because wireless activity may affect devices beyond the intended target.
OSWP Exam Reporting Requirements
Reporting is one of the most important subjects in this OSWP Exam Review.
OffSec requires a professional report describing the assessment work performed against the relevant scenarios.
The report must include sufficient technical detail and supporting evidence for the examiner to evaluate the submitted findings.
According to the official requirements, documentation must include the relevant wireless keys, commands, console output, and required proof evidence. The report must be submitted as a PDF.
What Should an OSWP Report Include?
A clear reporting structure can include:
- Assessment overview and scope.
- Scenario identification and network details.
- Testing methodology.
- Technical observations and evidence.
- Required screenshots and results.
- Conclusions for each scenario.
Candidates must follow the exact evidence and submission requirements in the official exam guide.
For public-facing study notes or example reports, remove credentials, wireless keys, proof values, and other sensitive information.
Read the official OSWP Exam Guide for the current reporting requirements.
OSWP Exam Review: Tools and Restrictions
OffSec permits appropriate manual wireless assessment tools, including the Aircrack-ng suite.
However, the official guide prohibits tools that automatically identify and execute wireless attacks with minimal interaction. Examples include Wifite, Wifiphisher, and Besside-ng.
AI chatbots and large language models are also prohibited during the active examination.
This distinction is important: candidates may use appropriate study resources before the exam, but must comply with OffSec’s rules while taking it.
Do not assume that a tool is permitted simply because it is commonly used in wireless penetration testing.
How to Prepare for OSWP in 2026
A useful OSWP Exam Review should lead to a realistic preparation plan.
Build Wireless Networking Fundamentals
Begin with IEEE 802.11 terminology, encryption types, authentication concepts, wireless channels, and Linux networking.
Make sure you understand what the tools are measuring rather than only how their interfaces work.
Complete the PEN-210 Curriculum
Use OffSec’s current PEN-210 training as your primary reference.
Review the modules, complete authorized exercises, and maintain notes that explain important concepts in your own words.
Practice With Compatible Hardware
For home practice, use equipment you own or are explicitly authorized to assess.
OffSec’s PEN-210 FAQ discusses compatible wireless adapters and notes that course exercises may require an access point and an injection-capable wireless card.
The examination itself provides a remote environment, so home-lab hardware requirements should not be confused with exam-day requirements.
Prepare a Reporting Template
Create a clear PDF reporting template before the exam.
Organize sections for observations, technical evidence, screenshots, and results so that documentation does not become an afterthought.
Review the Official Rules
Before scheduling, confirm the current exam duration, permitted tools, evidence requirements, and submission procedure.
The OffSec OSWP Exam FAQ provides additional guidance.
Is OSWP Worth It in 2026?
OSWP can be valuable for professionals whose responsibilities include wireless network assessments, infrastructure security, penetration testing, or red team engagements.
Its main advantage is specialization.
OSCP provides broader penetration testing coverage, while OSWP focuses specifically on wireless technologies and their security implications.
For someone who rarely works with wireless infrastructure, OSWP may be less relevant than a certification aligned with their primary responsibilities.
For professionals regularly evaluating enterprise Wi-Fi, however, the PEN-210 curriculum offers directly applicable knowledge.
OSWP Study Materials and Preparation Resources
CyberServices.Store provides OSWP-related digital resources for candidates interested in supplementary study materials and technical reports.
When evaluating third-party resources, check their stated contents, publication date, technical coverage, and delivery conditions.
Study materials should help candidates understand wireless security concepts and reporting methodology rather than promise guaranteed examination success.
For additional certification comparisons, see our Best Penetration Testing Certifications Guide.
OSWP Exam Review FAQ
Is OSWP difficult?
OSWP difficulty depends on your wireless networking knowledge, Linux experience, tool familiarity, and ability to work within the exam time limit.
How long is the OSWP exam?
The practical exam lasts 3 hours and 45 minutes, followed by an additional 24 hours for report submission.
How many scenarios must I complete to pass OSWP?
Candidates must complete two of the three available wireless scenarios, including the mandatory scenario.
Does OSWP require a penetration testing report?
Yes. OffSec requires a professional PDF report with technical documentation and supporting evidence.
Is OSWP a multiple-choice exam?
No. OSWP is a hands-on practical examination involving wireless network security assessments.
Can I use Wifite during the OSWP exam?
No. OffSec explicitly prohibits Wifite and similar automated wireless attack tools during the examination.
Can I use ChatGPT during the OSWP exam?
No. OffSec prohibits AI chatbots and large language models during the active examination.
Do I need a wireless adapter for PEN-210?
For home laboratory exercises, OffSec recommends compatible wireless hardware. The remote exam environment provides the equipment required for its scenarios.
Is OSWP worth taking after OSCP?
It can be worthwhile if you want to specialize in wireless penetration testing. OSWP and OSCP assess different areas of offensive security.
What is the best way to prepare for OSWP?
Complete PEN-210, strengthen wireless networking fundamentals, practice in authorized laboratories, become familiar with permitted tools, and prepare a reporting workflow.
Final Verdict: OSWP Exam Review 2026
This OSWP Exam Review highlights a focused practical certification that rewards wireless networking knowledge, technical accuracy, and clear documentation.
The exam is shorter than many advanced penetration testing assessments, but candidates still need to demonstrate independent skills under time pressure.
For professionals interested in wireless infrastructure security, OSWP provides a relevant specialization. The strongest preparation combines official PEN-210 training, authorized hands-on practice, and careful attention to the examination rules.
Vendor: https://www.offsec.com/courses/pen-210/
OSWP Exam Updates (Last Year – Today)
Over the last year, the OSWP (Offensive Security Wireless Professional) exam has remained stable in both structure and intent. The exam is still a hands-on practical assessment focused on real-world wireless network attacks. There have been no significant changes to the exam format or core objectives during this period.
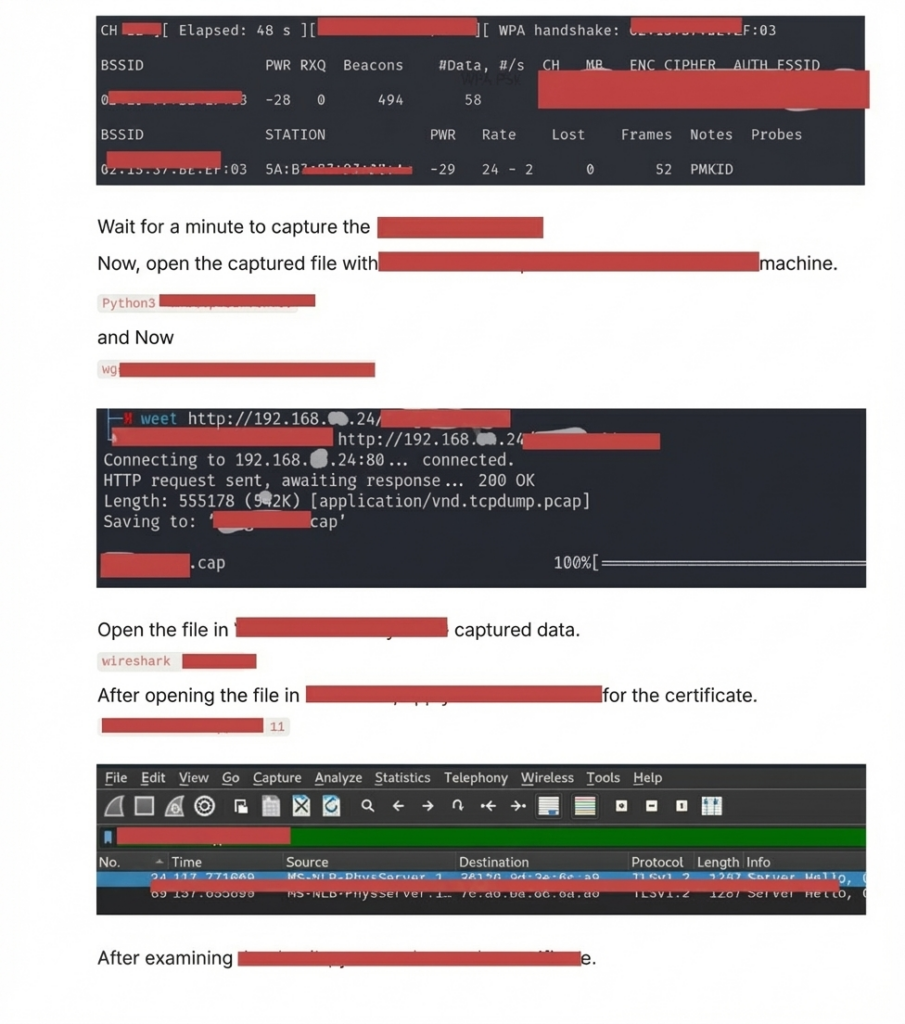
The OSWP content is still fully relevant. Candidates are expected to demonstrate a solid understanding of wireless fundamentals, including 802.11 protocols, encryption mechanisms (WEP, WPA/WPA2), and common misconfigurations. Practical skills such as packet capture, traffic analysis, handshake cracking, and exploiting weak wireless setups remain central to the exam. While wireless security tools continue to evolve, the exam continues to prioritize conceptual understanding and correct attack methodology over blind tool usage.
Candidates should be especially careful with environment setup and accuracy. Small mistakes in interface configuration, channel selection, or capture technique can waste valuable time. A methodical approach, clean note-taking, and clear documentation of each step are critical. Since the exam is very focused, knowing exactly when and how to apply each technique can make the difference between passing and failing.
Overall, OSWP remains a focused and practical certification for professionals working with wireless security and penetration testing.
Yes, the OSWP exam is still valid and respected in 2026. It continues to be a recognized certification for demonstrating hands-on wireless penetration testing skills.
There have been no major format changes. Recent updates mainly reflect improvements in exam clarity and environment realism, while the technical scope and hands-on nature of the exam remain the same.